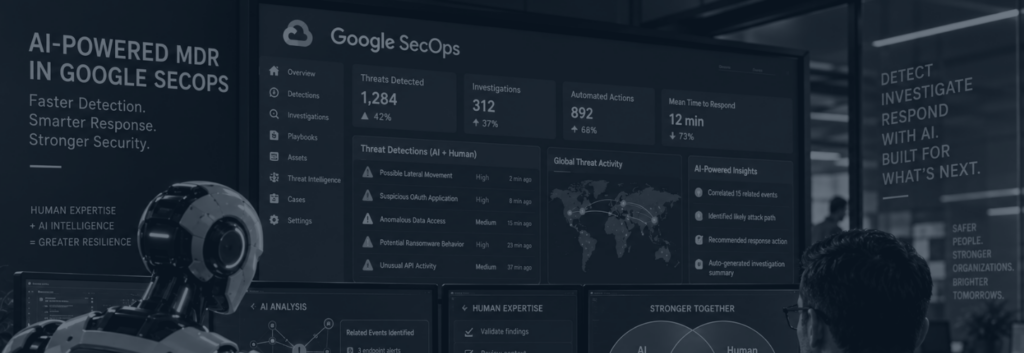
AI-Powered MDR With Google SecOps: Reduce Breach Risk
Date
Authors
Tony UV
Follow Us


Introduction: A New Era in Threat Detection and Response
Modern cyber threats move faster than traditional SOC teams can respond. Organizations relying on legacy SIEM tools often struggle with alert fatigue, slow detection, and fragmented visibility.
AI-powered Managed Detection and Response (MDR) changes this equation. By combining Google SecOps with detection engineering and automation, organizations can reduce breach risk by up to 70% while dramatically improving detection and response times.
This article explains how AI-driven MDR works, why Google SecOps is redefining SIEM, and how enterprises can operationalize faster, smarter security outcomes.
What is AI-Powered MDR?
AI-powered Managed Detection and Response (MDR) is a cybersecurity service that uses artificial intelligence, automation, and threat intelligence to detect, investigate, and respond to threats in real time.
Key capabilities include:
- Automated threat detection using behavioral analytics
- AI-assisted investigation and alert triage
- Integrated threat intelligence from sources like Mandiant and VirusTotal
- Automated response workflows (SOAR)
Key Results of a MDR + Google SecOps
Organizations using this model achieve:
- Mean Time to Detect (MTTD): reduced from days to under 8 hours
- Mean Time to Respond (MTTR): improved by 50%
- False positives: reduced below 10%
- Analyst productivity: increased by 35%
- Breach risk: reduced by up to 70%
Why Google SecOps is Transforming MDR
Google SecOps modernizes SIEM and SOAR by combining:
- Massive-scale search and analytics from Google Cloud
- Threat intelligence from Mandiant and VirusTotal
- AI-powered investigation via Gemini
- Built-in automation for response orchestration
This eliminates traditional SIEM challenges like complexity, lack of context, and analyst fatigue.
A Platform That Multiplies MDR Efficiency
Google SecOps delivers scalability, automation, and speed, and turns that into measurable business outcomes.
Impact KPIs
| Metric | Before MDR Optimization | After MDR + Google SecOps | ||
|---|---|---|---|---|
| Mean Time to Detect (MTTD) | 2–3 days | Under 8 hours | ||
| Mean Time to Respond (MTTR) | 10–12 hours | 50% faster | ||
| False Positive Rate | 25–30% | Below 10% | ||
| Analyst Productivity | Baseline | +35% efficiency via automation | ||
| Breach Risk & Impact | High | Up to 70% reduction |
Through assistive automation, risk-based analytics, and AI-assisted investigation, we help SOC teams focus on decisions — not just data.
The Power Behind the Platform
Google SecOps delivers key capabilities that boost MDR service:
- Unified Visibility
A single view across hybrid/multi-cloud environments via the Unified Data Model (UDM). - Curated Detections & YARA-L Rules
Thousands of prebuilt detections aligned to MITRE ATT&CK for faster coverage. - Gemini AI Assistant
Natural-language queries, alert summarization, and auto-generation of detection logic. - Integrated Threat Intelligence
Real-time insights from Mandiant and VirusTotal to enrich triage and validation. - SOAR Capabilities
Automation workflows (inherited from Siemplify) enable rapid response at scale.
Why Gartner’s Recognition Matters
Gartner’s 2025 Magic Quadrant places Google SecOps highest in “Completeness of Vision”, especially for AI and workflow automation — directly aligning with the outcomes we deliver.
“Use of AI is a core competency for Google, and its SecOps platform offers strong AI functionality throughout many of the common activities and functions associated with SIEM operations. Its well-integrated automation capabilities add to this overall strength.”
For clients, this means:
- Faster MDR results
- Smarter threat detection
- More cost-effective security outcomes
All backed by a recognized industry
Conclusion: The Future of MDR Is Intelligence-Driven
The SOC of the future is agentic, where AI and automation augment human analysts to anticipate threats, not just react to them.
Clients Gain:
- Improved KPIs across detection & response
- 24/7 threat hunting powered by intelligence
- Automated containment and recovery
- Strategic insights mapped to business risk
MDR, powered by Google SecOps, transforms data into defense and defense into confidence.
FAQs About AI-Powered MDR
How does AI reduce breach risk?
AI reduces breach risk by detecting threats earlier, automating investigation, and enabling faster response—minimizing attacker dwell time.
What is the difference between MDR and SIEM?
SIEM collects and analyzes logs, while MDR provides active monitoring, threat hunting, and response services.
Why is Google SecOps different from traditional SIEM?
Google SecOps integrates AI, automation, and threat intelligence into a single platform, reducing complexity and improving response speed.
What industries benefit most from MDR?
Healthcare, finance, retail, and critical infrastructure benefit most due to high threat exposure and regulatory requirements.